You're comparing endpoint protection offers and every second datasheet says XDR. The next one says EDR, sometimes both. Prices are far apart, feature lists sound alike. What's the actual difference, and where is the money well spent for a company with 20, 50 or 200 employees?
One clarification first, because it explains a lot.
EDR vs. XDR: Why the Terms Are So Fuzzy
There is no binding definition of EDR or XDR. No standard, no certification body, no committee that decides which features a product must have to carry the label. The terms come from marketing and analyst reports, not from a specification.
That has a practical consequence: a vendor can leave out functionality and still call the product XDR. Likewise, a product labelled EDR may do more than a competitor with the bigger name. So never compare the label. Compare the actual capabilities: Which data sources are monitored? Which responses are possible? Who is watching?
With that in mind, the terms can still be sorted into something useful.
What EDR Does and Where It Stops
EDR stands for Endpoint Detection and Response. An agent runs on laptops, desktops and servers and watches what happens there: which processes start, which files are written, which network connections are opened, which changes are made to the system configuration.
The difference to classic antivirus is behaviour. Antivirus asks: do I know this file to be malicious? EDR asks: is what's happening right now suspicious? An Office document that suddenly launches a script that then reads out credentials stands out, even if none of the individual components is known malware.
The second part, response, typically includes:
- Isolating a machine from the network without shutting it down
- Killing processes and quarantining files
- Reconstructing the timeline of an incident: what happened first, what followed from it?
The limit of EDR is in the name: endpoint. It only sees what happens on the devices. It is blind to everything else:
- Sign-ins to Microsoft 365 or Google Workspace from an unknown device
- Changes to mail forwarding rules
- Activity in cloud consoles such as Azure or AWS
- Network traffic between devices without an agent, such as printers or control systems
An attacker who lands directly in your mailbox with stolen credentials never touches a single monitored endpoint. Your EDR reports nothing. Not because it's bad, but because it isn't looking there.
What XDR Promises
The X in XDR stands for Extended. The idea: don't just watch endpoints, but bring several sources together and relate them to each other. Typical sources are:
- Endpoints (what EDR delivers)
- Identities: sign-ins, MFA events, permission changes
- Email: phishing detection, suspicious attachments, forwarding rules
- Network: firewall logs, DNS queries, unusual connections
- Cloud workloads and SaaS applications
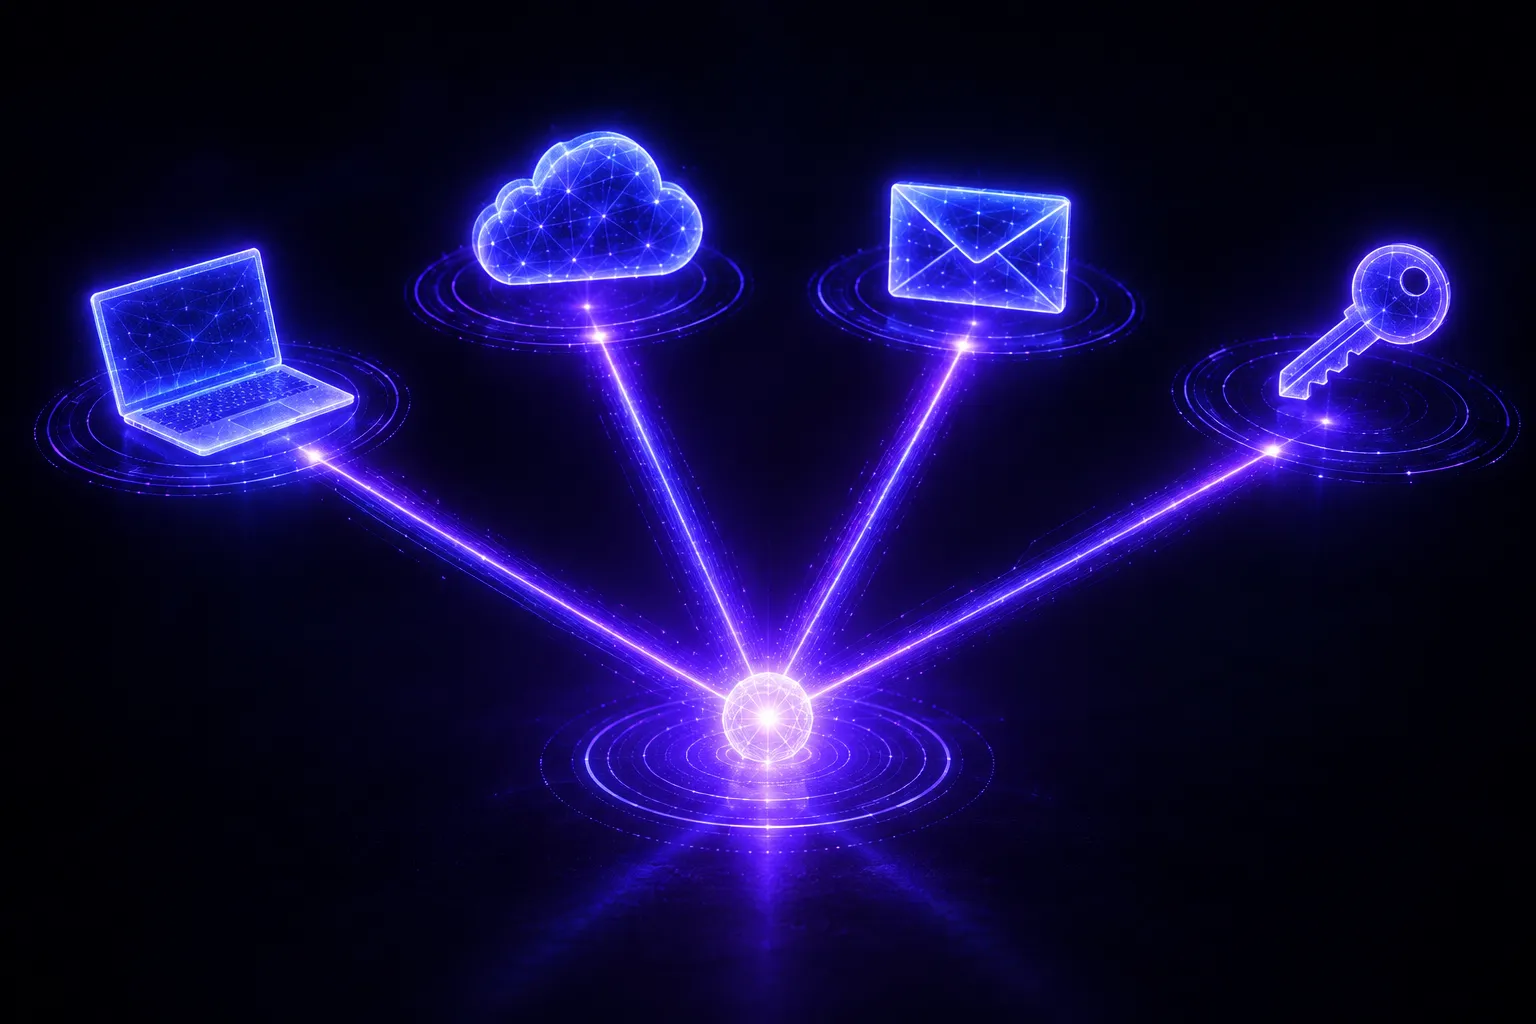
The real value is correlation. Three weak signals, each harmless on its own, form a clear picture together: a sign-in from an unusual country, shortly after that a new forwarding rule in the mailbox, then a download attempt on a laptop. Individually, none of them might trigger an alert. Together, that's an incident.
The response reaches further too: lock an account, end a session, block a sender, not just isolate a machine.
And this is where the fuzziness from the beginning comes back. Some products called XDR are essentially an EDR with an additional connector for email. Others genuinely cover identity, cloud and network. Both are allowed to call themselves XDR. So ask specifically:
- Which data sources are integrated natively, which only via interfaces?
- Are events correlated across sources or merely displayed side by side?
- Which responses can I trigger outside the endpoints?
- How long is data retained, and can I search back in time?
And Where Does SIEM Fit In?
Anyone looking into XDR quickly runs into a third term: SIEM, Security Information and Event Management. A SIEM collects logs from practically all systems, stores them long term and allows custom searches and rules. It's the open, flexible option: you decide which sources to connect, and you can ask any question the data can answer.
The flip side: a SIEM offers little ready-made detection out of the box. It needs rules, maintenance and people who work with the data. That's exactly where XDR steps in with pre-built, vendor-maintained logic, at the cost of less freedom in choosing sources.
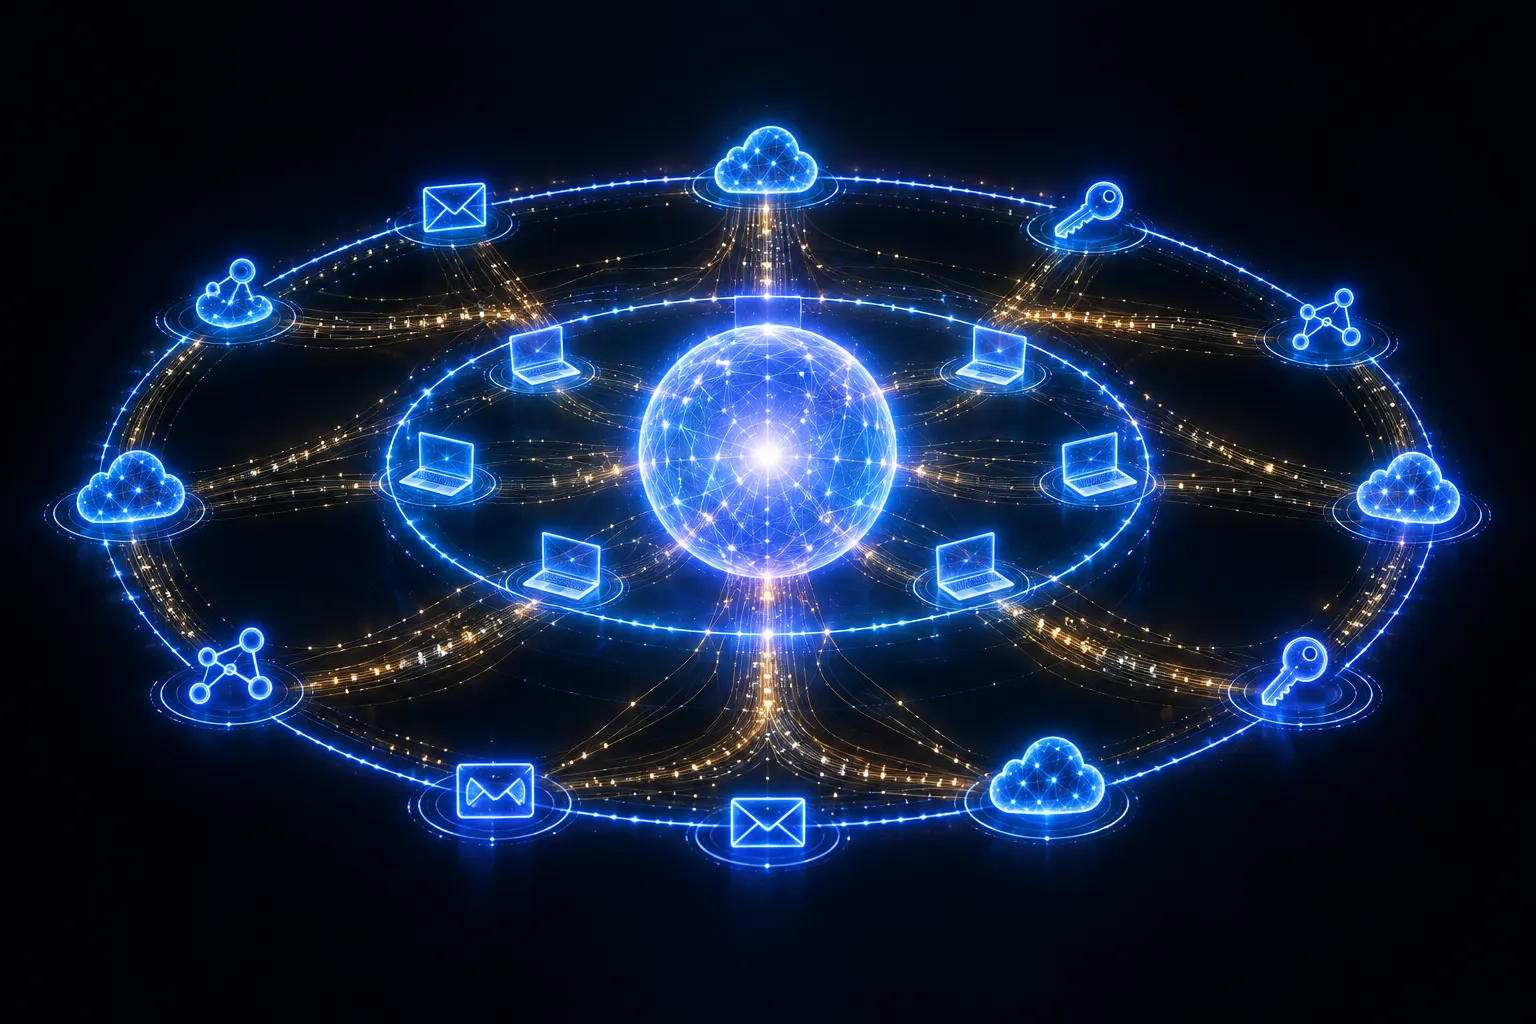
In our view, the two don't compete, they complement each other. That's why our platform is built as a SIEM/SOAR with XDR integration: our agent delivers the endpoint telemetry and the logs from all connected sources, the SIEM correlates across them, and the SOAR side makes sure a detection can be followed by a response right away, from the same interface. Because detection lives in the SIEM, we're not limited to the rule set a conventional XDR ships for the general case: our rule base goes well beyond that and can be tailored to your environment. Ready-made detection where it helps, open data where you have your own questions.
To be clear: no platform, ours included, works without being tuned to your environment and without someone handling the alerts. Anyone who sells it differently is promising too much.
What SMEs Actually Need
EDR or XDR is really the wrong question. The right one is: where would an attack start in your company, and would you see it?
For most SMEs, that leads to a clear order of priorities:
- Complete endpoint coverage. Every laptop, every server, including the Mac and Linux machines and the test box in the basement. An unmonitored device is the gap someone walks through.
- Visibility into identities. If your company runs on Microsoft 365 or Google Workspace, the login is your real perimeter. Sign-ins and rule changes there need to be monitored, whether by an XDR or a separate solution.
- Someone who responds. An alert at three in the morning that nobody reads doesn't help. Define who watches, how quickly and with what authority. Internal or external, both work, but it has to be defined.
- Retention and traceability. If you discover an incident three weeks later, you need the data from back then. Check how long it's kept.
- A test. Have someone verify that detection actually fires in a real scenario. A penetration test or a targeted attack simulation shows in a few days what months of normal operation hide.
As a rule of thumb:
- Small team, everything on laptops and M365, little infrastructure of your own: a solid EDR plus identity monitoring covers the essentials, provided the response is organised.
- Own servers, cloud workloads, several sites or regulatory requirements: here, correlation across sources pays off. An XDR or SIEM combination makes sense because separate tools side by side quickly become hard to oversee.
And for both: the best tool nobody operates loses to a simpler one that someone runs seriously.
Conclusion
EDR and XDR are not protected terms. Look behind the label: which sources are monitored, is there correlation, which responses are possible, who works with it. EDR is the foundation and a good start for many SMEs, but it stays blind to identity, cloud and email. XDR closes that gap, if it genuinely brings several sources together rather than just carrying the name.
If you're unsure what's missing in your environment, we'll find out together. In a consulting session we go through your systems and tell you openly where you stand and what you need, even if the answer is: less than you thought. Or contact us directly with your question. An overview of what we do is on our services page.