Almost every vendor puts Zero Trust on their data sheet these days. Firewalls, VPNs, identity solutions, even printers advertise it. That makes the term hard to pin down, and many managing directors and IT leads rightly ask: is this a product I need to buy? A standard? Or just another buzzword?
In short: Zero Trust is a principle, not a product. And it matters so much because the assumption most company networks are built on no longer holds.
The old assumption: safe inside, dangerous outside
Classic IT security works like a castle. Outside, the wall: firewall and VPN. Inside, the courtyard, where everyone moves freely. Once you are in, whether by cable in the office or by VPN from home, you are considered trustworthy. Servers, file shares, printers and databases are reachable from the internal network, often without any further check.
This model made sense when all employees sat in the office, all servers stood in the basement and the only way into the network went through the firewall. Today none of that is true:
- Your data lives in Microsoft 365, in a software vendor's cloud and on laptops in home offices.
- External IT partners, suppliers and freelancers have access to the network.
- Attackers no longer come through the wall. They come through the gate with a valid password.
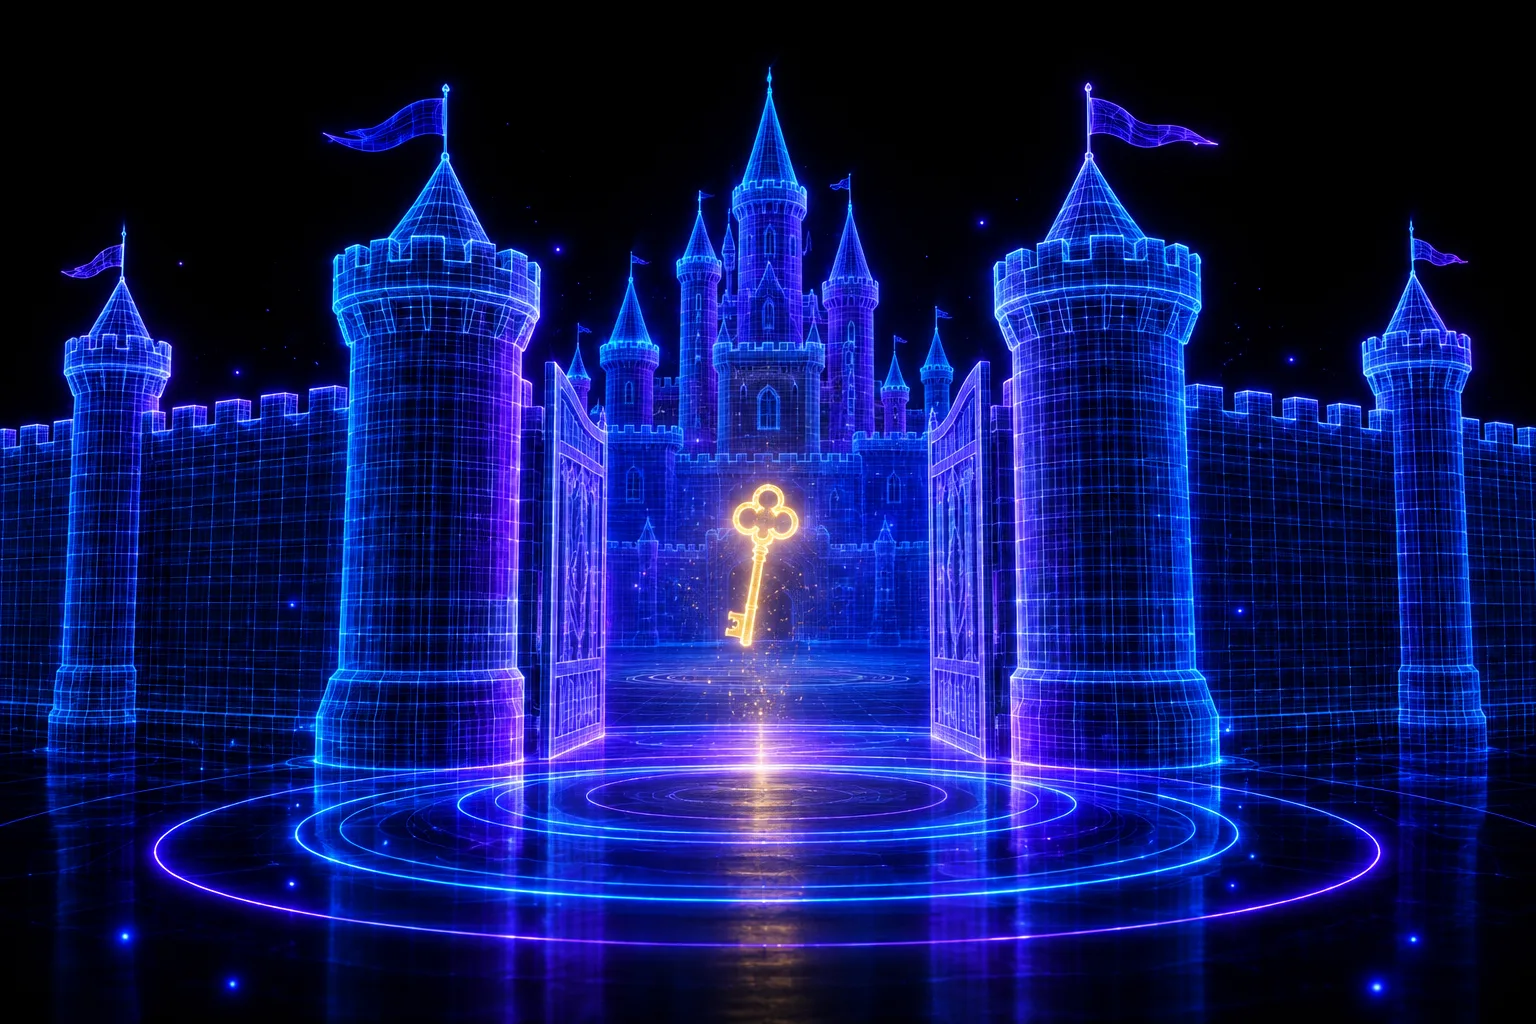
The last point is decisive. In most incidents we support, nobody cracked a firewall. The attacker had credentials: from a phishing email, from a data breach at another service, from a poorly secured remote access. Once inside the network, the castle opened every door for them. That is exactly the standard pattern for ransomware groups like Akira: first an access, then days of movement through the network, then encryption.
What Zero Trust does differently
Zero Trust reverses the assumption. Location on the network says nothing about whether a request is trustworthy. Every access is checked, whether it comes from inside or outside. The term dates from 2010, and the description in common use today comes from the US standard NIST SP 800-207. In practice it boils down to three rules:
- Verify every access explicitly. Who are you, which device are you coming from, is that device healthy, and are you allowed to do what you are about to do? These questions are asked on every access, not just at login in the morning.
- As few rights as possible. An account gets access to what it needs for its task and nothing more. Accounting does not need access to the development servers, and an admin does not work with admin rights all day.
- Assume an attacker is already inside. The network is built so that a compromised device or account can do as little damage as possible. Segmentation, logging and detection are not extras but part of the design.
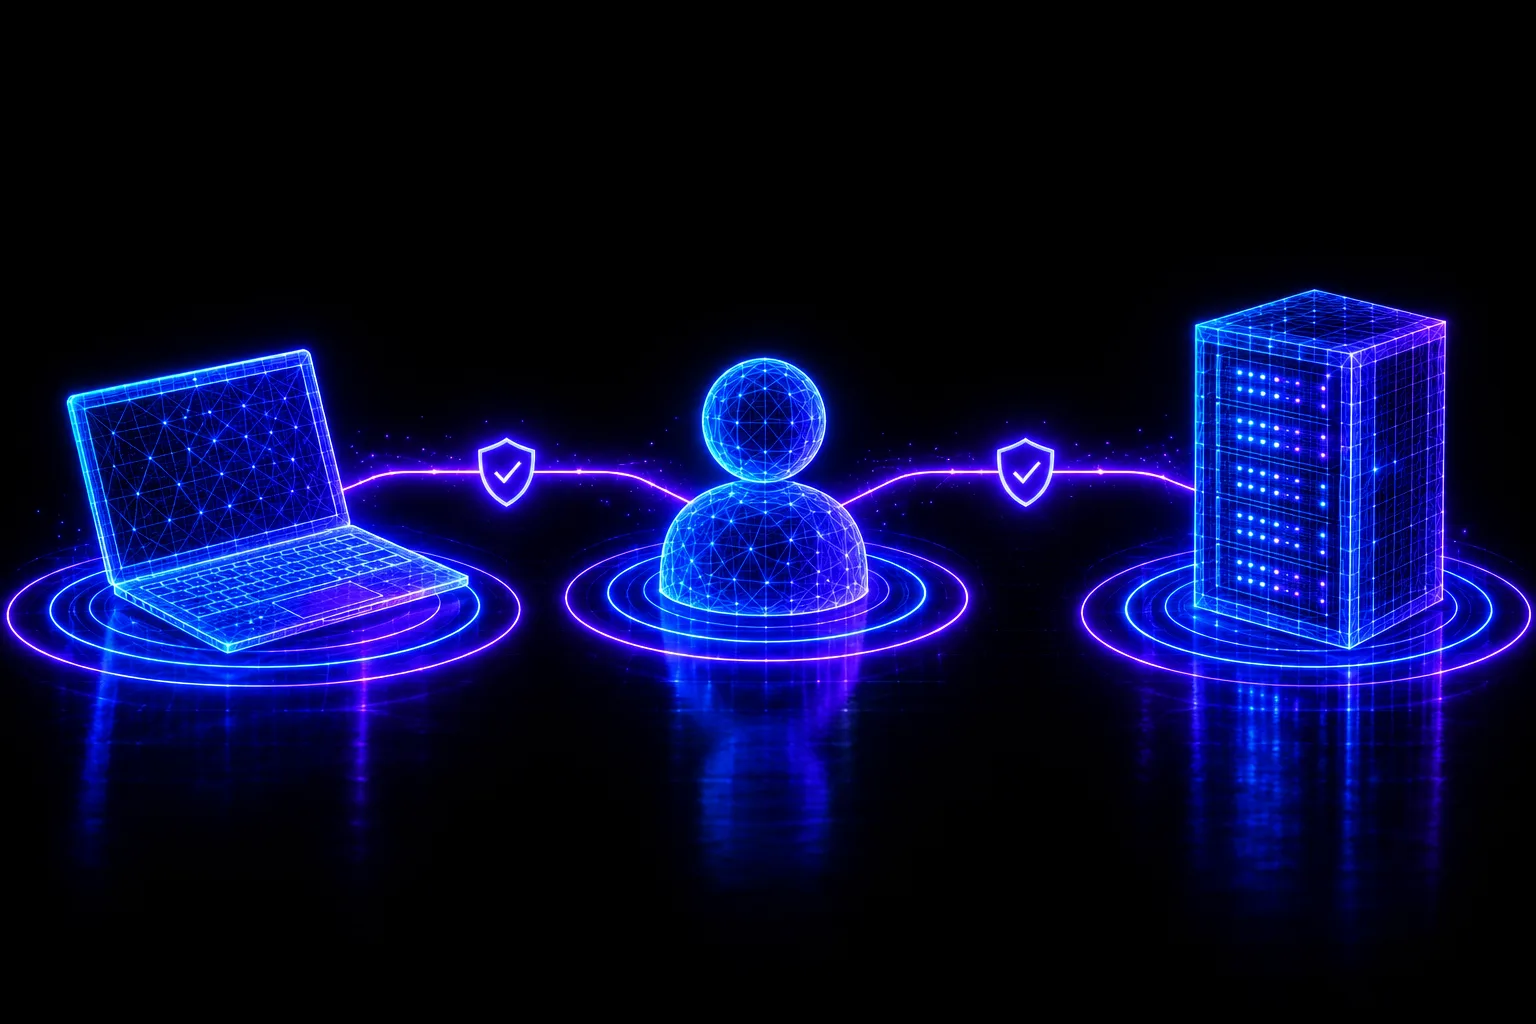
Importantly, Zero Trust does not mean nobody is allowed to do anything anymore. It means trust is not granted wholesale, but per access and based on facts.
Why this matters right now
Three developments have turned the topic from an enterprise concern into an SME concern in recent years.
The attackers have adapted. Ransomware groups work in a division of labour, industrially. Credentials are traded, the actual attack runs by the playbook. An SME with 50 employees is no longer too small a target, but a convenient one.
The network has no edge anymore. Cloud, home office and external partners have riddled the castle wall with holes. A VPN that gives every connected device full access is more of a risk than a protection today.
Insurers and regulators demand it. Cyber insurers ask about multi-factor authentication, rights management and segmentation. NIS2 reaches Swiss suppliers through supply chains. The revised Swiss data protection act requires appropriate technical measures. All three come down to the same principles.
What Zero Trust is not
A few clarifications, because there is a lot of marketing in this space:
- Not a product. No single tool makes your company "Zero Trust". Vendors sell building blocks for it, some good, some just renamed firewalls.
- Not a project with an end date. It is a way of thinking about access. You start and get better step by step.
- Not a replacement for the basics. Backups, updates and awareness remain. Zero Trust complements them by limiting the damage when one of those basics fails.
Where an SME should sensibly start
The full textbook implementation is neither necessary nor affordable for an SME. The biggest effect comes from a few steps that can be implemented in weeks rather than years:
- Multi-factor authentication everywhere. On Microsoft 365 or Google Workspace, on the VPN, on every admin access. Without MFA every stolen password is an open gate. This is the measure with the best ratio of effort to impact.
- Separate admin rights. Nobody works with an admin account day to day. Admin rights live on separate accounts, ideally only for the duration of the task.
- Rethink remote access. Instead of a VPN leading into the whole network, access per application. Whoever only needs time tracking only gets time tracking.
- Segment the network. Servers, workstations, guest Wi-Fi and production systems belong in separate zones. An infected laptop must not reach the domain controller directly.
- See what is happening. Zero Trust assumes an attacker could be inside. Then you also need to be able to detect them: central logging of logins, permission changes and endpoint activity, and someone who handles the alerts.
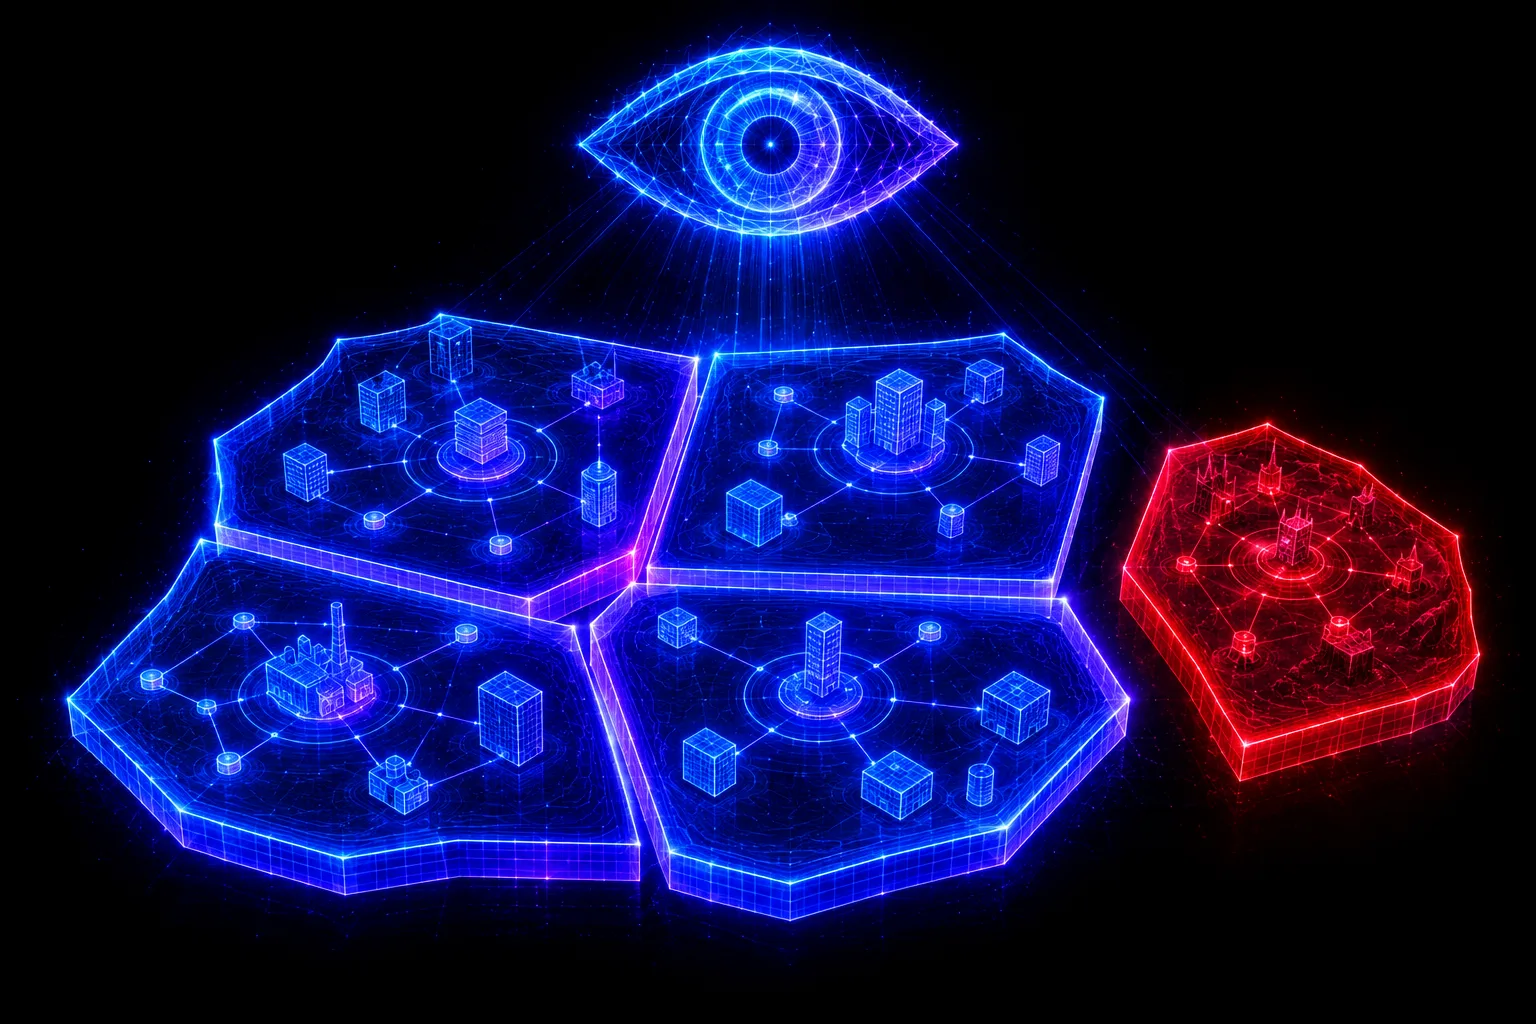
The fifth point is often forgotten. Verifying and restricting is one half, observing and responding is the other. That is exactly what we built Spectacles for: it collects events from endpoints, identities and cloud, detects when an account suddenly behaves differently, and can isolate an affected system before the attacker moves on.
Conclusion
Zero Trust is the answer to a simple observation: the company network perimeter no longer protects, because attackers come through the gate with valid credentials. The principle against it is just as simple: verify every access, keep rights small, assume someone is inside, and therefore keep watching.
For an SME this does not mean rebuilding IT. It means starting with MFA, separate admin rights and visibility, and following up with the rest step by step. If you want to know where your company stands, a Security Health Check shows you the gaps with priorities, and an architecture review delivers the target picture for the rebuild. Or bring your questions to a consulting session.